Hello,
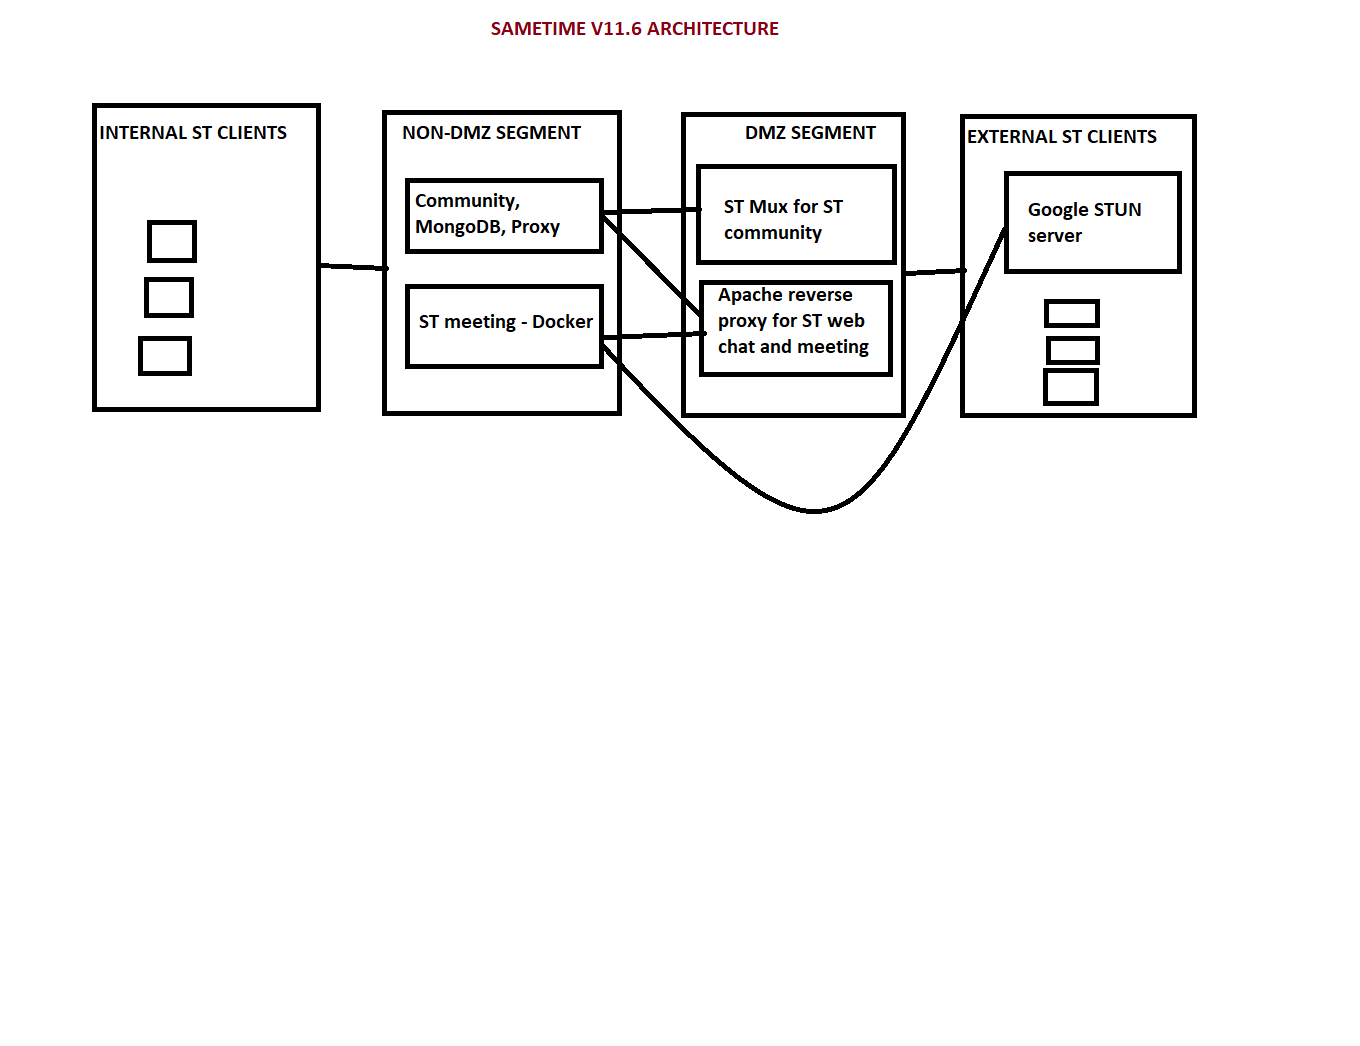
We have planned to install Sametime chat & meeting components on DC & DR clustering and we would be placing the ST Chat and meeting components on the NON-DMZ segment and placing the Apache reverse proxy and ST Mux on the DMZ segment.
Please refer to the sample Sametime architecture picture.
Internal and external ST clients would be accessing the ST web chat and web meeting through Apache reverse proxy and ST mux.
If the Sametime goes down on the DC site then we would be doing the manual DNS record changes to switch to the DR site.
Can you please advise whether this will work or not and suggest the best practice?
Also kindly suggest what would be an alternate option if the customer is unable to allow the port opening from Sametime meeting server to Google stun server.
Thank you in advance.
Regards,
Elango
Hi Elango,
There are a couple of good resources for you for planning:
1) See the help center, there are some suggestions for DMZ and external users: https://help.hcltechsw.com/sametime/11.6/admin/topology.html
Please note that the Sametime proxy, mux, and meeting servers are all designed to have internet users, and you don't need a reverse proxy. Clients need direct unimpeded access to the meeting server and the STUN server.
2) The Sametime deployment webinar replay, it was for Sametime 11.5, but the same applies for version 11.6. https://register.gotowebinar.com/register/5931368659988254476?source=DSAcademyBlog
3) The customer can install their own STUN server, if they are unable to use Google's service. All users will need access to it. https://help.hcltechsw.com/sametime/11.6/admin/session_traversal_utilities.html
Let us know if you have a specific question.
Thanks,
Casey
Thank you for your update.
Hi Elango,
how exactly do you define "external ST clients"?
Are these users, who do not belong to your company (i.e. they are your customers or your business partners) or are these employees of your company, who are physically and from a network perspective located "externally" (e.g. employees in a homeoffice location)?
What Sametime clients should these "external ST clients" use...only a web browser or also the Sametime Mobile app? Should they also use Sametime Connect clients? If not, then there is no need to have ST MUX running in the DMZ.
Thanks
Erik
Thank you for your response.
Yes, you are correct, employees in a home office location. For work from home users.
Thanks for your reply.
If these employees in a home office location use the Sametime Connect client (either embedded in Notes or standalone), then placing ST MUX in the DMZ is certainly an option to get them connected. If they don't use the Sametime Connect client (i.e. they only use a browser or the ST mobile app), then you don't need ST MUX in the DMZ, only ST Proxy.
As an alternative, you could also connect these employees to your organizations internal network via a VPN solution such as HCL SafeLinx.
As Casey already pointed out, make sure your clients have direct access to the meeting server and the STUN server.
Thank you so much for your suggestions.